artabramov/hidden
Encrypted self-hosted S3-compatible object storage for sensitive data.
759
artabramov/hidden repository overview
Hidden S3 — encrypted self-hosted S3 storage
Hidden S3 is S3-compatible object storage for sensitive data on privately managed infrastructure. It provides filesystem-level encryption independently of the S3 layer while maintaining full S3 compatibility.
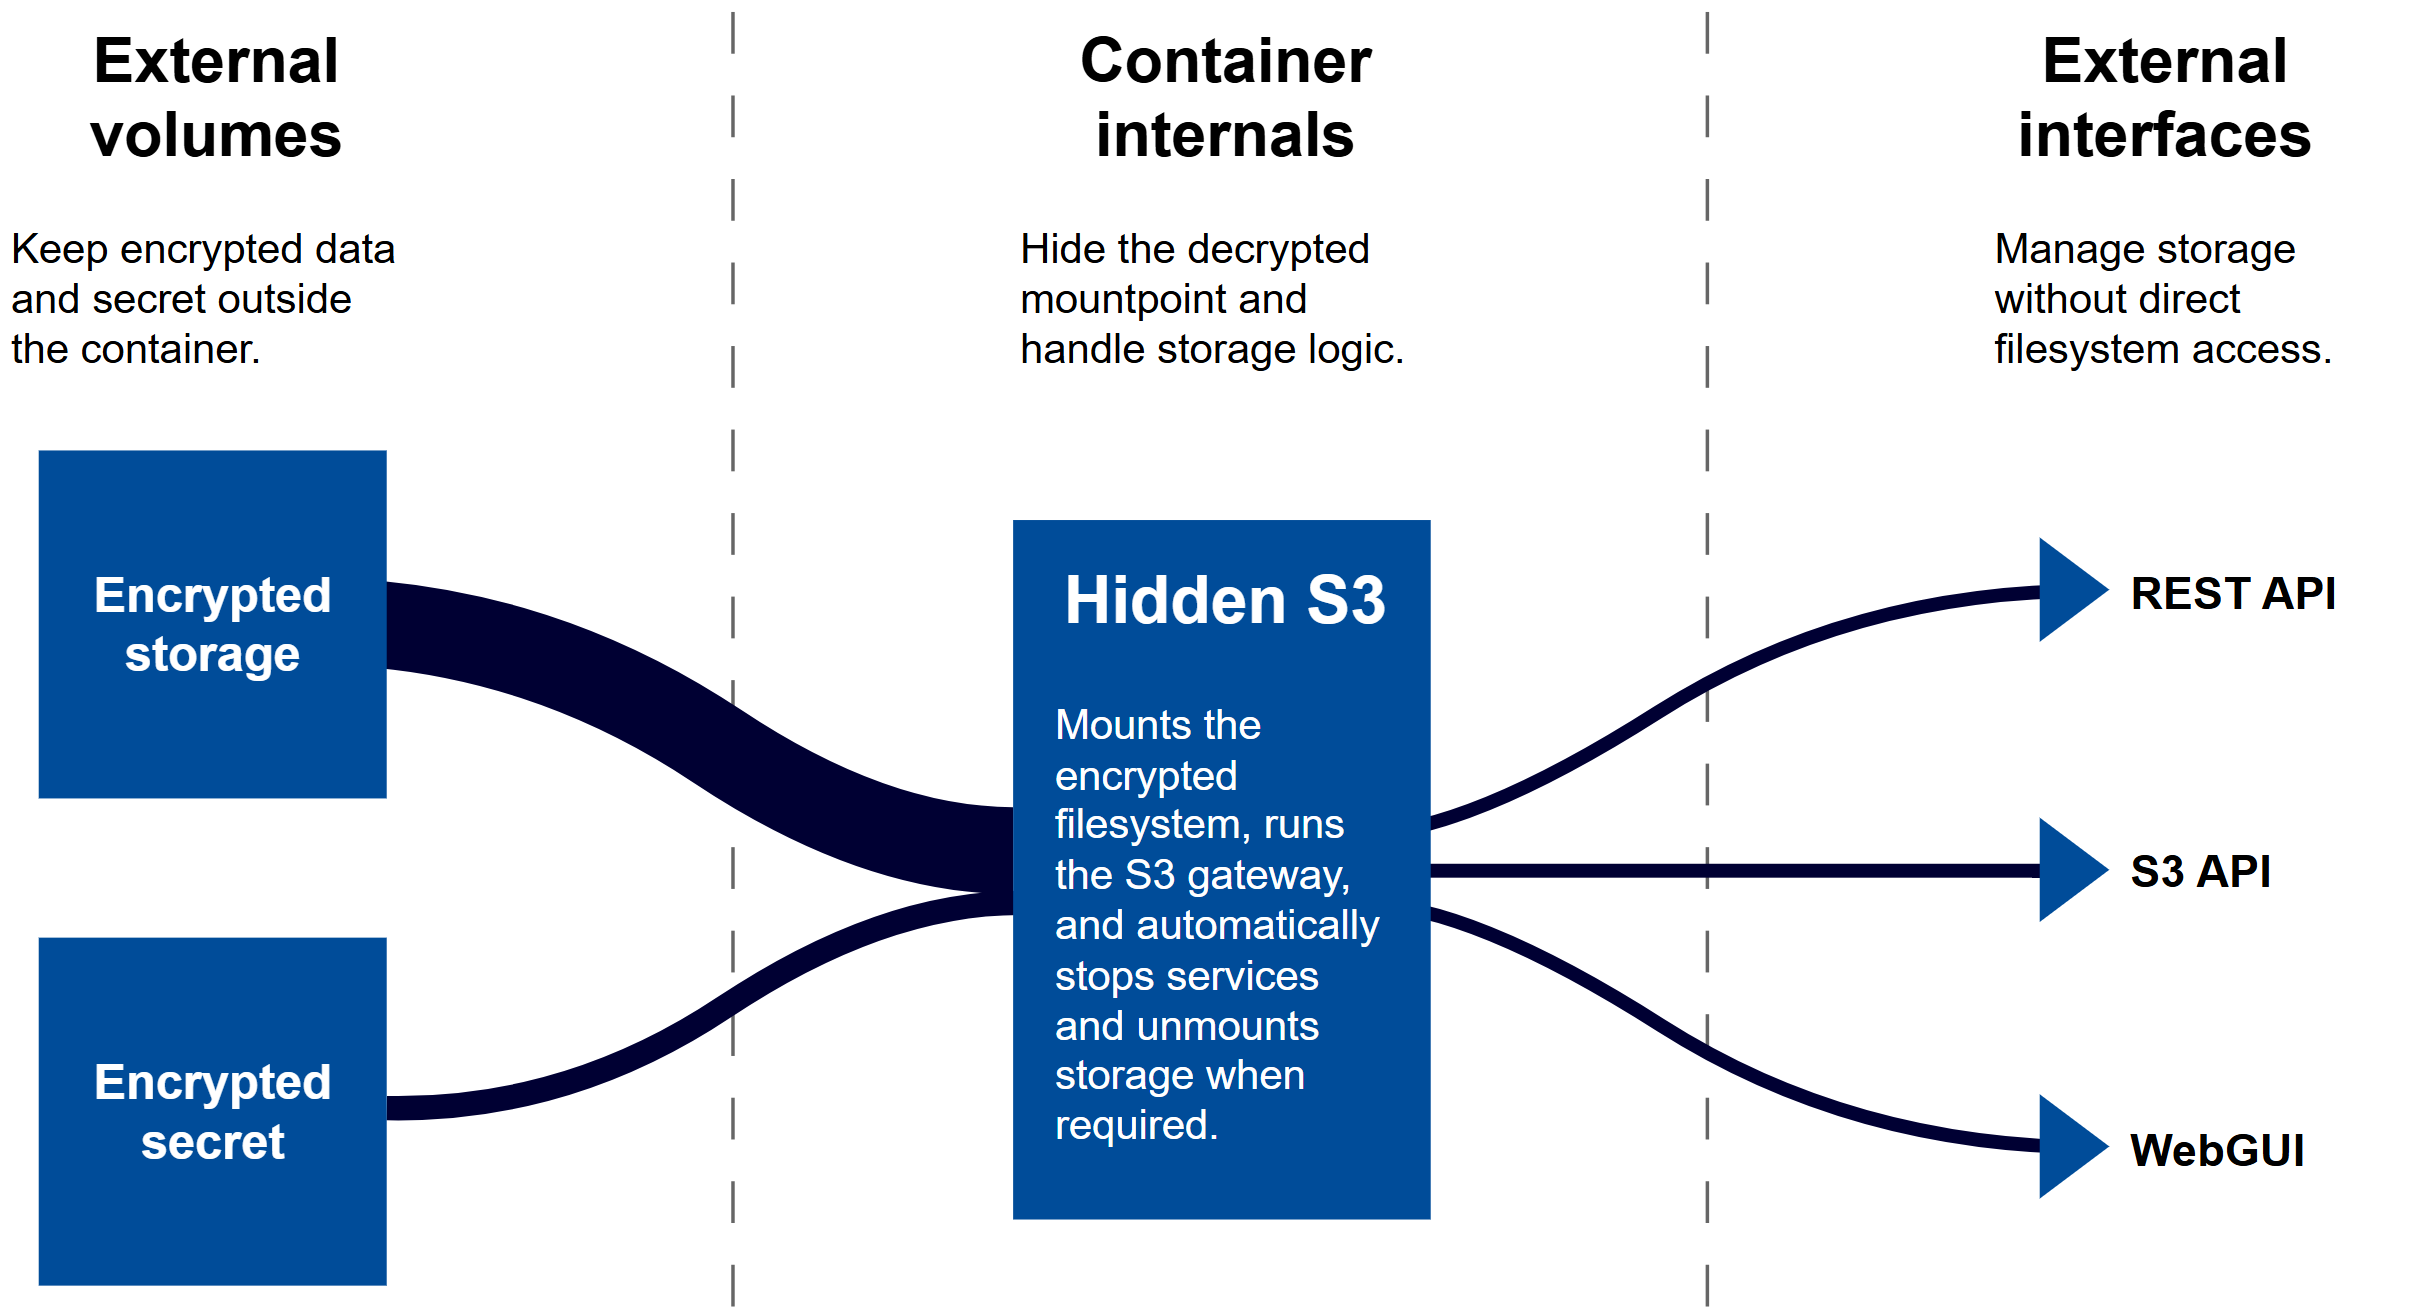
Built on gocryptfs and VersityGW, the system combines encrypted storage with an S3-compatible gateway. VersityGW provides the S3 API, IAM, and WebGUI, while a REST management API controls the encrypted storage lifecycle.
References
Quick start
Prepare the host directory for application secrets:
sudo mkdir -p /mnt/hidden/secrets
sudo mount --bind /mnt/hidden /mnt/hidden
sudo mount --make-shared /mnt/hidden
For stronger separation, mount removable media or remote storage at /mnt/hidden/secrets before starting the container.
Download the latest image:
docker pull artabramov/hidden:latest
Create and run the container:
docker run -d \
  --init \
  --restart unless-stopped \
  --cap-add SYS_ADMIN \
  --device /dev/fuse \
  --security-opt apparmor:unconfined \
  -p 8081:8081 \
  -p 9000:9000 \
  -p 8080:8080 \
  -v hidden-cipherdir:/var/lib/cipherdir \
  --mount type=bind,source=/mnt/hidden,target=/var/lib/hidden,bind-propagation=rslave \
  --name hidden \
  artabramov/hidden:latest
Open the management interface to initialize and mount encrypted storage:
REST API: http://localhost:8081/docs
Once storage is mounted:
S3 API: http://localhost:9000
WebGUI: http://localhost:8080
How it works
S3 data and IAM state reside within the encrypted filesystem. Decrypted data is available only while the filesystem is mounted and is accessible externally only through the S3 API.
Initialization, mounting, unmounting, and other operations on the encrypted storage require both the secrets volume to be available and the master password to be provided. If either is unavailable, the storage remains protected.
As an additional protection layer, a watchdog monitors critical runtime conditions. If the application process fails, the secrets volume becomes unavailable, or the storage itself becomes inaccessible, it automatically unmounts the decrypted filesystem and stops the S3 gateway.
License
Apache License 2.0
Tag summary
Content type
Image
Digest
sha256:a9e14fcbd…
Size
102.8 MB
Last updated
3 days ago
docker pull artabramov/hidden