djerfy/htrace
Archived
💻 Swiss Army knife for http/https troubleshooting and profiling.
Image
1
7.6K
djerfy/htrace repository overview
Created by
trimstray and
contributors
Description
htrace.sh is a shell script for http/https troubleshooting and profiling. It's also a simple wrapper around several open source security tools.
For a more detailed understanding of htrace.sh, its parameters, functions and how it all works, see the Wiki.
Preview
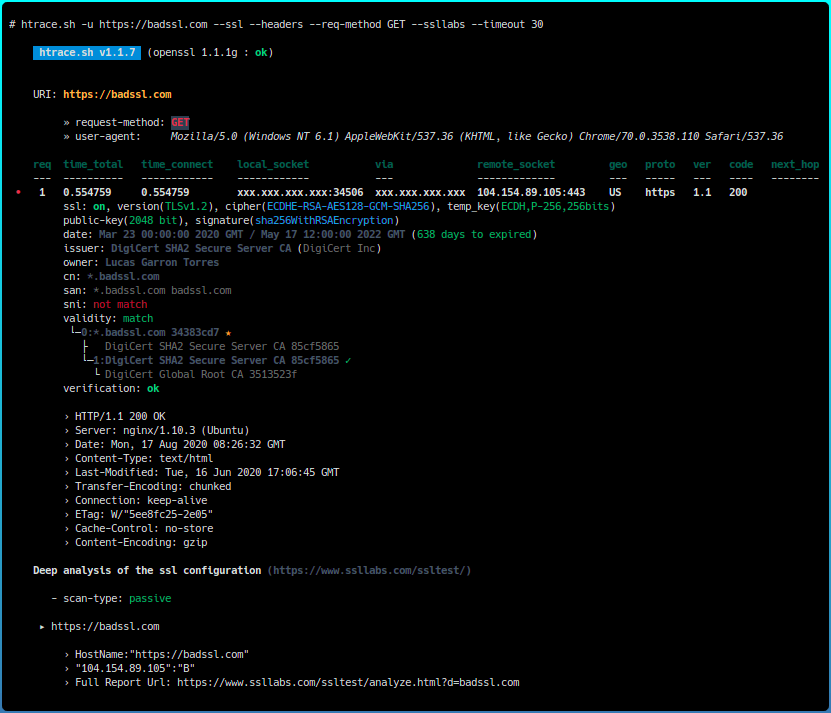
Parameters
Provides the following options:
    htrace.sh v1.1.5

  Usage:

    htrace.sh <option|long-option> [value]

  Examples:

    htrace.sh -u https://example.com -s -h -b
    htrace.sh -u https://example.com --all-scans

  Options:

        --help                                show this message
        --version                             show script version
        --examples                            show script examples

    Standard:

        -u|--url <value>                      set target url with http/https protocol
        -s|--ssl                              show basic ssl server/connection parameters
        -h|--headers                          show response headers
        -b|--body                             show response body
        -M|--req-method <value>               set request method (default: GET)
        -H|--req-header <value>               set request header(s)
        -p|--proxy <value>                    set proxy server (not for external tools)
        -r|--resolve <value>                  resolve the host+port to this address
        -i|--iface <value>                    set network interface (or address)
        -a|--all-scans                        use all external security tools

    Security tools:

        --testssl                             test ssl protocols and ciphers (testssl.sh)
        --observatory                         analyze website headers (mozilla observatory)
        --ssllabs                             deep analysis of the ssl web server (ssllabs)
        --mixed-content                       scan website for non-secure resources (mixed-content-scan)
        --nse                                 scan website and domain with nse library (nmap)
        --waf                                 detect and bypass web application firewalls (whatwaf)
        --dns                                 enumerate subdomains (subfinder) and perform zone transfer

    Extended:

        --cache-bypass <value>                try (proxy) cache bypass
        --user-agent <value>                  set 'User-Agent' header
        --referer <value>                     set 'Referer' header
        --auth <value>                        set authentication method
        --tlsv <value>                        set tls version
        --ciph <value>                        set of cryptographic algorithm
        --max-redirects <num>                 set max redirects (default: 10)
        --timeout <num>                       set max timeout (default: 15)
        --hide-src-ip                         hide source ip from output
License
GPLv3 : http://www.gnu.org/licenses/
Free software, Yeah!
Tag summary
Content type
Image
Digest
Size
117.3 MB
Last updated
over 5 years ago
docker pull djerfy/htrace