dyonr/qbittorrentvpn
Runs a qBittorent-nox client with an optional WireGuard or OpenVPN connection
1M+
dyonr/qbittorrentvpn repository overview
qBittorrent, WireGuard and OpenVPN
Docker container which runs the latest qBittorrent-nox client while connecting to WireGuard or OpenVPN with iptables killswitch to prevent IP leakage when the tunnel goes down.
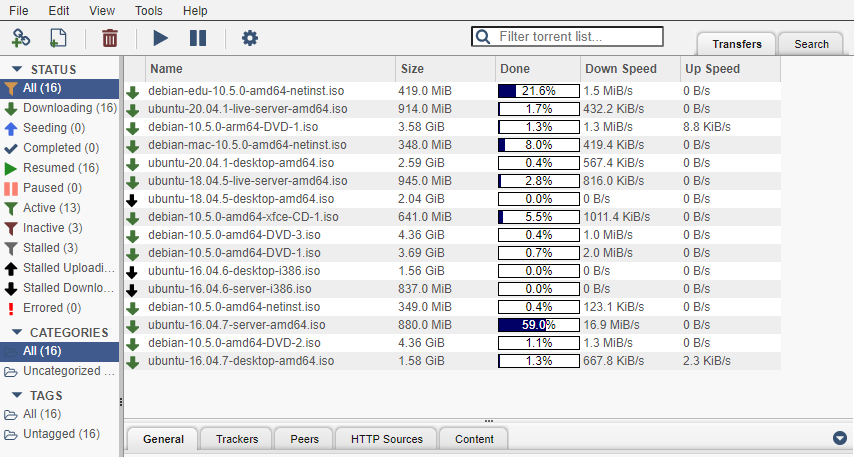
Docker Features
- Base: Debian 10-slim
- qBittorrent compiled from source
- libtorrent compiled from source
- Compiled with the latest version of Boost
- Compiled with the latest versions of CMake
- Selectively enable or disable WireGuard or OpenVPN support
- IP tables killswitch to prevent IP leaking when VPN connection fails
- Configurable UID and GID for config files and /downloads for qBittorrent
- Created with Unraid in mind
- BitTorrent port 8999 exposed by default
Run container from Docker registry
The container is available from the Docker registry and this is the simplest way to get it
To run the container use this command, with additional parameters, please refer to the Variables, Volumes, and Ports section:
$ docker run --privileged  -d \
              -v /your/config/path/:/config \
              -v /your/downloads/path/:/downloads \
              -e "VPN_ENABLED=yes" \
              -e "VPN_TYPE=wireguard" \
              -e "LAN_NETWORK=192.168.0.0/24" \
              -p 8080:8080 \
              --restart unless-stopped \
              dyonr/qbittorrentvpn
Variables, Volumes, and Ports
Environment Variables
| Variable | Required | Function | Example | Default |
|---|---|---|---|---|
VPN_ENABLED | Yes | Enable VPN (yes/no)? | VPN_ENABLED=yes | yes |
VPN_TYPE | Yes | WireGuard or OpenVPN (wireguard/openvpn)? | VPN_TYPE=wireguard | openvpn |
VPN_USERNAME | No | If username and password provided, configures ovpn file automatically | VPN_USERNAME=ad8f64c02a2de | |
VPN_PASSWORD | No | If username and password provided, configures ovpn file automatically | VPN_PASSWORD=ac98df79ed7fb | |
LAN_NETWORK | Yes (atleast one) | Comma delimited local Network's with CIDR notation | LAN_NETWORK=192.168.0.0/24,10.10.0.0/24 | |
ENABLE_SSL | No | Let the container handle SSL (yes/no)? | ENABLE_SSL=yes | yes |
NAME_SERVERS | No | Comma delimited name servers | NAME_SERVERS=1.1.1.1,1.0.0.1 | 1.1.1.1,1.0.0.1 |
PUID | No | UID applied to /config files and /downloads | PUID=99 | 99 |
PGID | No | GID applied to /config files and /downloads | PGID=100 | 100 |
UMASK | No | UMASK=002 | 002 | |
HEALTH_CHECK_HOST | No | This is the host or IP that the healthcheck script will use to check an active connection | HEALTH_CHECK_HOST=one.one.one.one | one.one.one.one |
HEALTH_CHECK_INTERVAL | No | This is the time in seconds that the container waits to see if the internet connection still works (check if VPN died) | HEALTH_CHECK_INTERVAL=300 | 300 |
HEALTH_CHECK_SILENT | No | Set to 1 to supress the 'Network is up' message. Defaults to 1 if unset. | HEALTH_CHECK_SILENT=1 | 1 |
INSTALL_PYTHON3 | No | Set this to yes to let the container install Python3. | INSTALL_PYTHON3=yes | no |
ADDITIONAL_PORTS | No | Adding a comma delimited list of ports will allow these ports via the iptables script. | ADDITIONAL_PORTS=1234,8112 |
Volumes
| Volume | Required | Function | Example |
|---|---|---|---|
config | Yes | qBittorrent, WireGuard and OpenVPN config files | /your/config/path/:/config |
downloads | No | Default downloads path for saving downloads | /your/downloads/path/:/downloads |
Ports
| Port | Proto | Required | Function | Example |
|---|---|---|---|---|
8080 | TCP | Yes | qBittorrent WebUI | 8080:8080 |
8999 | TCP | Yes | qBittorrent TCP Listening Port | 8999:8999 |
8999 | UDP | Yes | qBittorrent UDP Listening Port | 8999:8999/udp |
Access the WebUI
Access https://IPADDRESS:PORT from a browser on the same network. (for example: https://192.168.0.90:8080)
Default Credentials
| Credential | Default Value |
|---|---|
username | admin |
password | adminadmin |
How to use WireGuard
The container will fail to boot if VPN_ENABLED is set and there is no valid .conf file present in the /config/wireguard directory. Drop a .conf file from your VPN provider into /config/wireguard and start the container again. The file must have the name wg0.conf.
How to use OpenVPN
The container will fail to boot if VPN_ENABLED is set and there is no valid .ovpn file present in the /config/openvpn directory. Drop a .ovpn file from your VPN provider into /config/openvpn and start the container again. You may need to edit the ovpn configuration file to load your VPN credentials from a file by setting auth-user-pass.
Note: The script will use the first ovpn file it finds in the /config/openvpn directory. Adding multiple ovpn files will not start multiple VPN connections.
Example auth-user-pass option for .ovpn files
auth-user-pass credentials.conf
Example credentials.conf
username
password
PUID/PGID
User ID (PUID) and Group ID (PGID) can be found by issuing the following command for the user you want to run the container as:
id <username>
Issues
If you are having issues with this container please submit an issue on GitHub. Please provide logs, docker version and other information that can simplify reproducing the issue. Using the latest stable verison of Docker is always recommended. Support for older version is on a best-effort basis.
Credits:
MarkusMcNugen/docker-qBittorrentvpn
DyonR/jackettvpn
This projects originates from MarkusMcNugen/docker-qBittorrentvpn, but forking was not possible since DyonR/jackettvpn uses the fork already.
Tag summary
Content type
Image
Digest
sha256:d5c50beb5…
Size
166.9 MB
Last updated
almost 3 years ago
docker pull dyonr/qbittorrentvpn