flyingfrares/taskflaw
Vulnerable Web App for DevSecOps Testing
Image
Security
Web servers
0
479
flyingfrares/taskflaw repository overview
taskflaw
The goal of this project is to build an infrastructure that follows the DevOps pipeline while incorporating Security (Sec) practices. This includes:
- Containerization
- CI/CD Pipelines
- Deployment & Provisioning
- Security Testing
- Monitoring
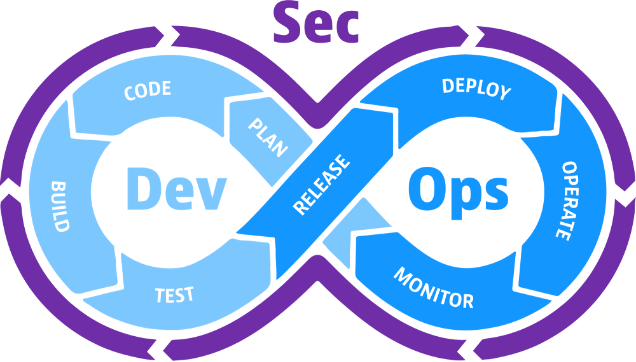
The Software used as the sandbox environment is a fork of the tonimobin/cyber-security-base-2022 repository. It is a simple note/task Web App with basic CRUD functionalities, written in Python using Django framework. This version has been intentionally modified to include several common security vulnerabilities found in Web Applications. These flaws are based on the OWASP Top 10 list.
Tag summary
Content type
Image
Digest
sha256:5af6dad64…
Size
57.5 MB
Last updated
over 1 year ago
docker pull flyingfrares/taskflaw