fors33/l3dgr
Local by default cryptographic integrity for Docker-shared paths under /host.
460
fors33/l3dgr repository overview
L3dgr


Docker Desktop extension from Fors33 for cryptographic data integrity on operator-selected paths: scan, verify, and seal. Live ingest uses T3thr. Product docs: fors33.com/l3dgr/docs.
Legal: L3dgr supports integrity checks and audit preparation only. It does not certify compliance with SEC Rule 17a-4(f) or any other regulatory framework. See LEGAL_DISCLAIMER.md and fors33.com/legal.
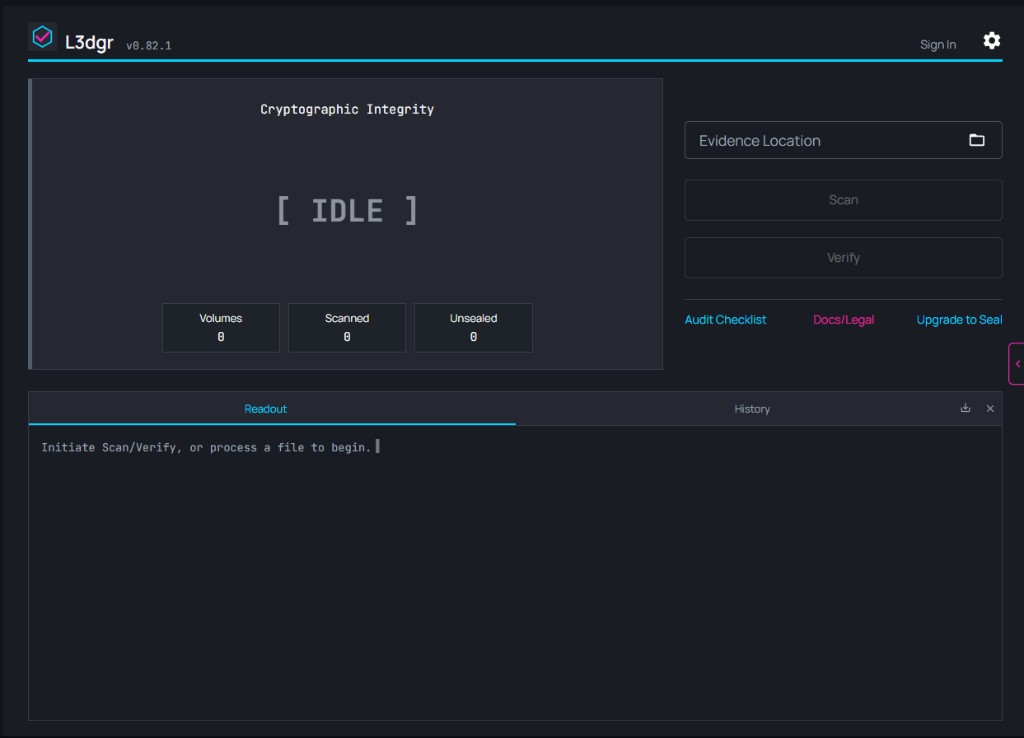
Table of Contents
- Features
- Requirements
- Quick start
- Privacy and data lifecycle
- Related tools
- L3dgr Beta
- Support
- Compliance
- License
Features
- Scan and verify operator-selected Docker-shared folders with deterministic hash comparison (no sampling).
- Seal licensed Dashboard workflows with manifests,
.f33sidecars, and receipts. - File processor for local CSV, JSON, and Parquet normalization via T3thr.
- Live ingest and scheduled jobs when your license includes pipeline connectors.
- Local by default: operator-selected paths, Docker named volumes, optional telemetry off until enabled in Settings.
Scan, verify, and attest are strictly deterministic: full directory traversal, no sampling or heuristic integrity; every conclusion is traceable to hash comparison or explicit enumeration. Probabilistic approaches are not used.
Requirements
- Docker Desktop on Windows, macOS, or Linux.
- Operator-selected folders shared with Docker Desktop so L3dgr can scan, verify, or process them.
- Lobby scan, verify, and file processing do not require sign-in. Dashboard Seal and live ingest require a licensed session.
Quick start
Install the current release candidate from Docker Hub. Docker Marketplace listing remains on hold. Pin this tag; :latest is not published.
docker extension install fors33/l3dgr:v0.82.1-rc.1
If L3dgr is already installed:
docker extension update -f fors33/l3dgr:v0.82.1-rc.1
In the extension:
- Lobby covers scan, verify, and file processing without sign-in.
- Dashboard Seal and live ingest require a licensed session.
Uninstall:
docker extension uninstall fors33/l3dgr
Before uninstall, use Settings → Advanced → Backup Identity and store the zip offline and encrypted. Uninstalling or deleting Docker volumes removes local identity, settings, staging, and audit state.
Privacy and data lifecycle
Dataset bytes, seals, and integrity artifacts stay on operator-selected paths and Docker named volumes (local-first data). Operator identity, license, and seat wrap use Fors33 account services except air-gapped entitlements. The extension runs inside the Docker Desktop extension VM and accesses host folders that the operator selects and Docker Desktop shares.
Local access and outputs:
- Reads shared host folders selected by the operator for scan, seal, verify, drift review, and file processing.
- Writes generated integrity artifacts to selected host paths or Docker-managed volumes, including
.f33sidecars, manifests, receipts, reports, audit events, staging JSONL, dead-letter JSONL, and optional CSV derivatives. - File-processor jobs expose Download actions for
accepted.jsonl,dead_letter.jsonl, and optionalaccepted.csvwhen artifacts are in the staging root. JSONL is the immutable source of truth; CSV is optional derivative output. - Stores extension state in Docker named volumes under
/var/lib/fors33, including preferences, operator identity material, license token, connection profiles, audit state, staging outputs, and cryptographic binding data.
Remote and account surfaces:
- OAuth sign-in and license sync contact Fors33 services for operator session and entitlement checks.
- Minimal technical telemetry is disabled by default. When enabled in Settings, it sends only event name, platform, timestamp, and success/error status.
- Telemetry does not include file paths, file contents, hashes, emails, OAuth tokens, license tokens, connector URLs, bucket names, environment variables, stack traces, or private keys.
- Remote S3/WORM storage and remote connectors are used only when configured by the operator. The operator controls the destination provider, bucket or endpoint, access rules, encryption, and retention policy. Independent time: Standard uses the host-synchronized VM clock and TSA is optional. Strict and Regulated require an operator RFC 3161 timestamp authority plus the in-image trust bundle, not the extension VM clock. Record durability for audit preparation is the operator's WORM destination (for example Object Lock) or reconstruction from the local append-only ledger. Use of this software does not certify SEC Rule 17a-4(f) or FDA 21 CFR Part 11.
Retention:
- Docker extension updates preserve named volumes.
- Uninstalling the extension or deleting its Docker volumes removes local identity, settings, staging, and audit state. Use Settings → Advanced → Backup Identity before destructive maintenance.
- Website-side retention for account, license, and telemetry records is governed by the Fors33 Terms of Service and Privacy Policy.
Related tools
Fors33 Verifier and Fors33 Scanner are MIT-licensed open tools. They run locally on your infrastructure. They do not use the L3dgr Docker Desktop extension airlock, L3dgr account OAuth, or L3dgr optional technical telemetry. They support integrity checks and audit preparation only. They do not certify compliance with SEC Rule 17a-4(f) or any other regulatory framework.
- Scan and verify on disk: Fors33 Scanner and Fors33 Verifier (no Docker Desktop).
- Seal, receipts, and epoch: L3dgr Dashboard Seal with a licensed operator session.
- CI: the Verifier and Scanner GitHub Actions on the packages below.
Docker Desktop is required for L3dgr (Seal, seats, live ingest). It is not required for independent scan and verify. Auditors do not need Docker Desktop.
pip install fors33-verifier==0.11.0
pip install fors33-scanner==0.10.0
docker pull fors33/fors33-verifier:v0.11.0
docker pull fors33/fors33-scanner:v0.10.0
- Verifier: GitHub · PyPI · Action
- Scanner: GitHub · PyPI · Action
- Ten-minute recipe: fors33.com/l3dgr
L3dgr Beta
Fors33 is running a closed L3dgr Beta cohort (legal ID L3DGR-BETA-1.9). This wave is Pro only. It is not an open promo code and not unlimited free Pro.
- Apply: fors33.com/l3dgr/beta
- Participant quick start: fors33.com/l3dgr/beta/guide
- Cohort status: fors33.com/l3dgr/beta/status
- Key delivery: fors33.com/l3dgr/setup
Approved participants complete checkout with a Fors33-issued promotion code, then finish required journeys: one Dashboard seal and one pipeline (file processor, live ingest, or scheduled job). Complimentary Pro access covers the program window. Graduation terms (including year-one discount for completed requirements) are in the offer email and L3DGR-BETA-1.9.
Support
- Docs: https://fors33.com/l3dgr/docs
- Support: https://fors33.com/l3dgr/support
- Account: https://fors33.com/account
- L3dgr Beta: [email protected]
- Extension changelog: CHANGELOG.md
Compliance
L3dgr supports cryptographic integrity checks, operator-attributed seals, and audit preparation. Use of this software does not establish, guarantee, or certify compliance with SEC Rule 17a-4(f), FDA 21 CFR Part 11, or any other regulatory framework. See LEGAL_DISCLAIMER.md and product docs at https://fors33.com/l3dgr/docs
License
MIT License. Copyright (c) 2026 Fors33, Inc. See LICENSE.
Product documents (current IDs in the legal manifest): L3DGR-EULA-2.5, L3DGR-PRIVACY-2.10. L3dgr Beta participants also accept L3DGR-BETA-1.9.
Legal and regulatory boundaries: LEGAL_DISCLAIMER.md and fors33.com/legal.
Tag summary
Content type
Image
Digest
sha256:5cbd8cb6d…
Size
128.2 MB
Last updated
26 minutes ago
docker pull fors33/l3dgr:sha256-5cbd8cb6de2f7d0b25987d5a08c7da354bda628223c2d4272ca42ba5c8c18f32