fullstackspectrum/forgely
Forgely is a security graph visualization engine which works against Cloudsmith.
200
fullstackspectrum/forgely repository overview
Forgely
From artifact to blast radius.
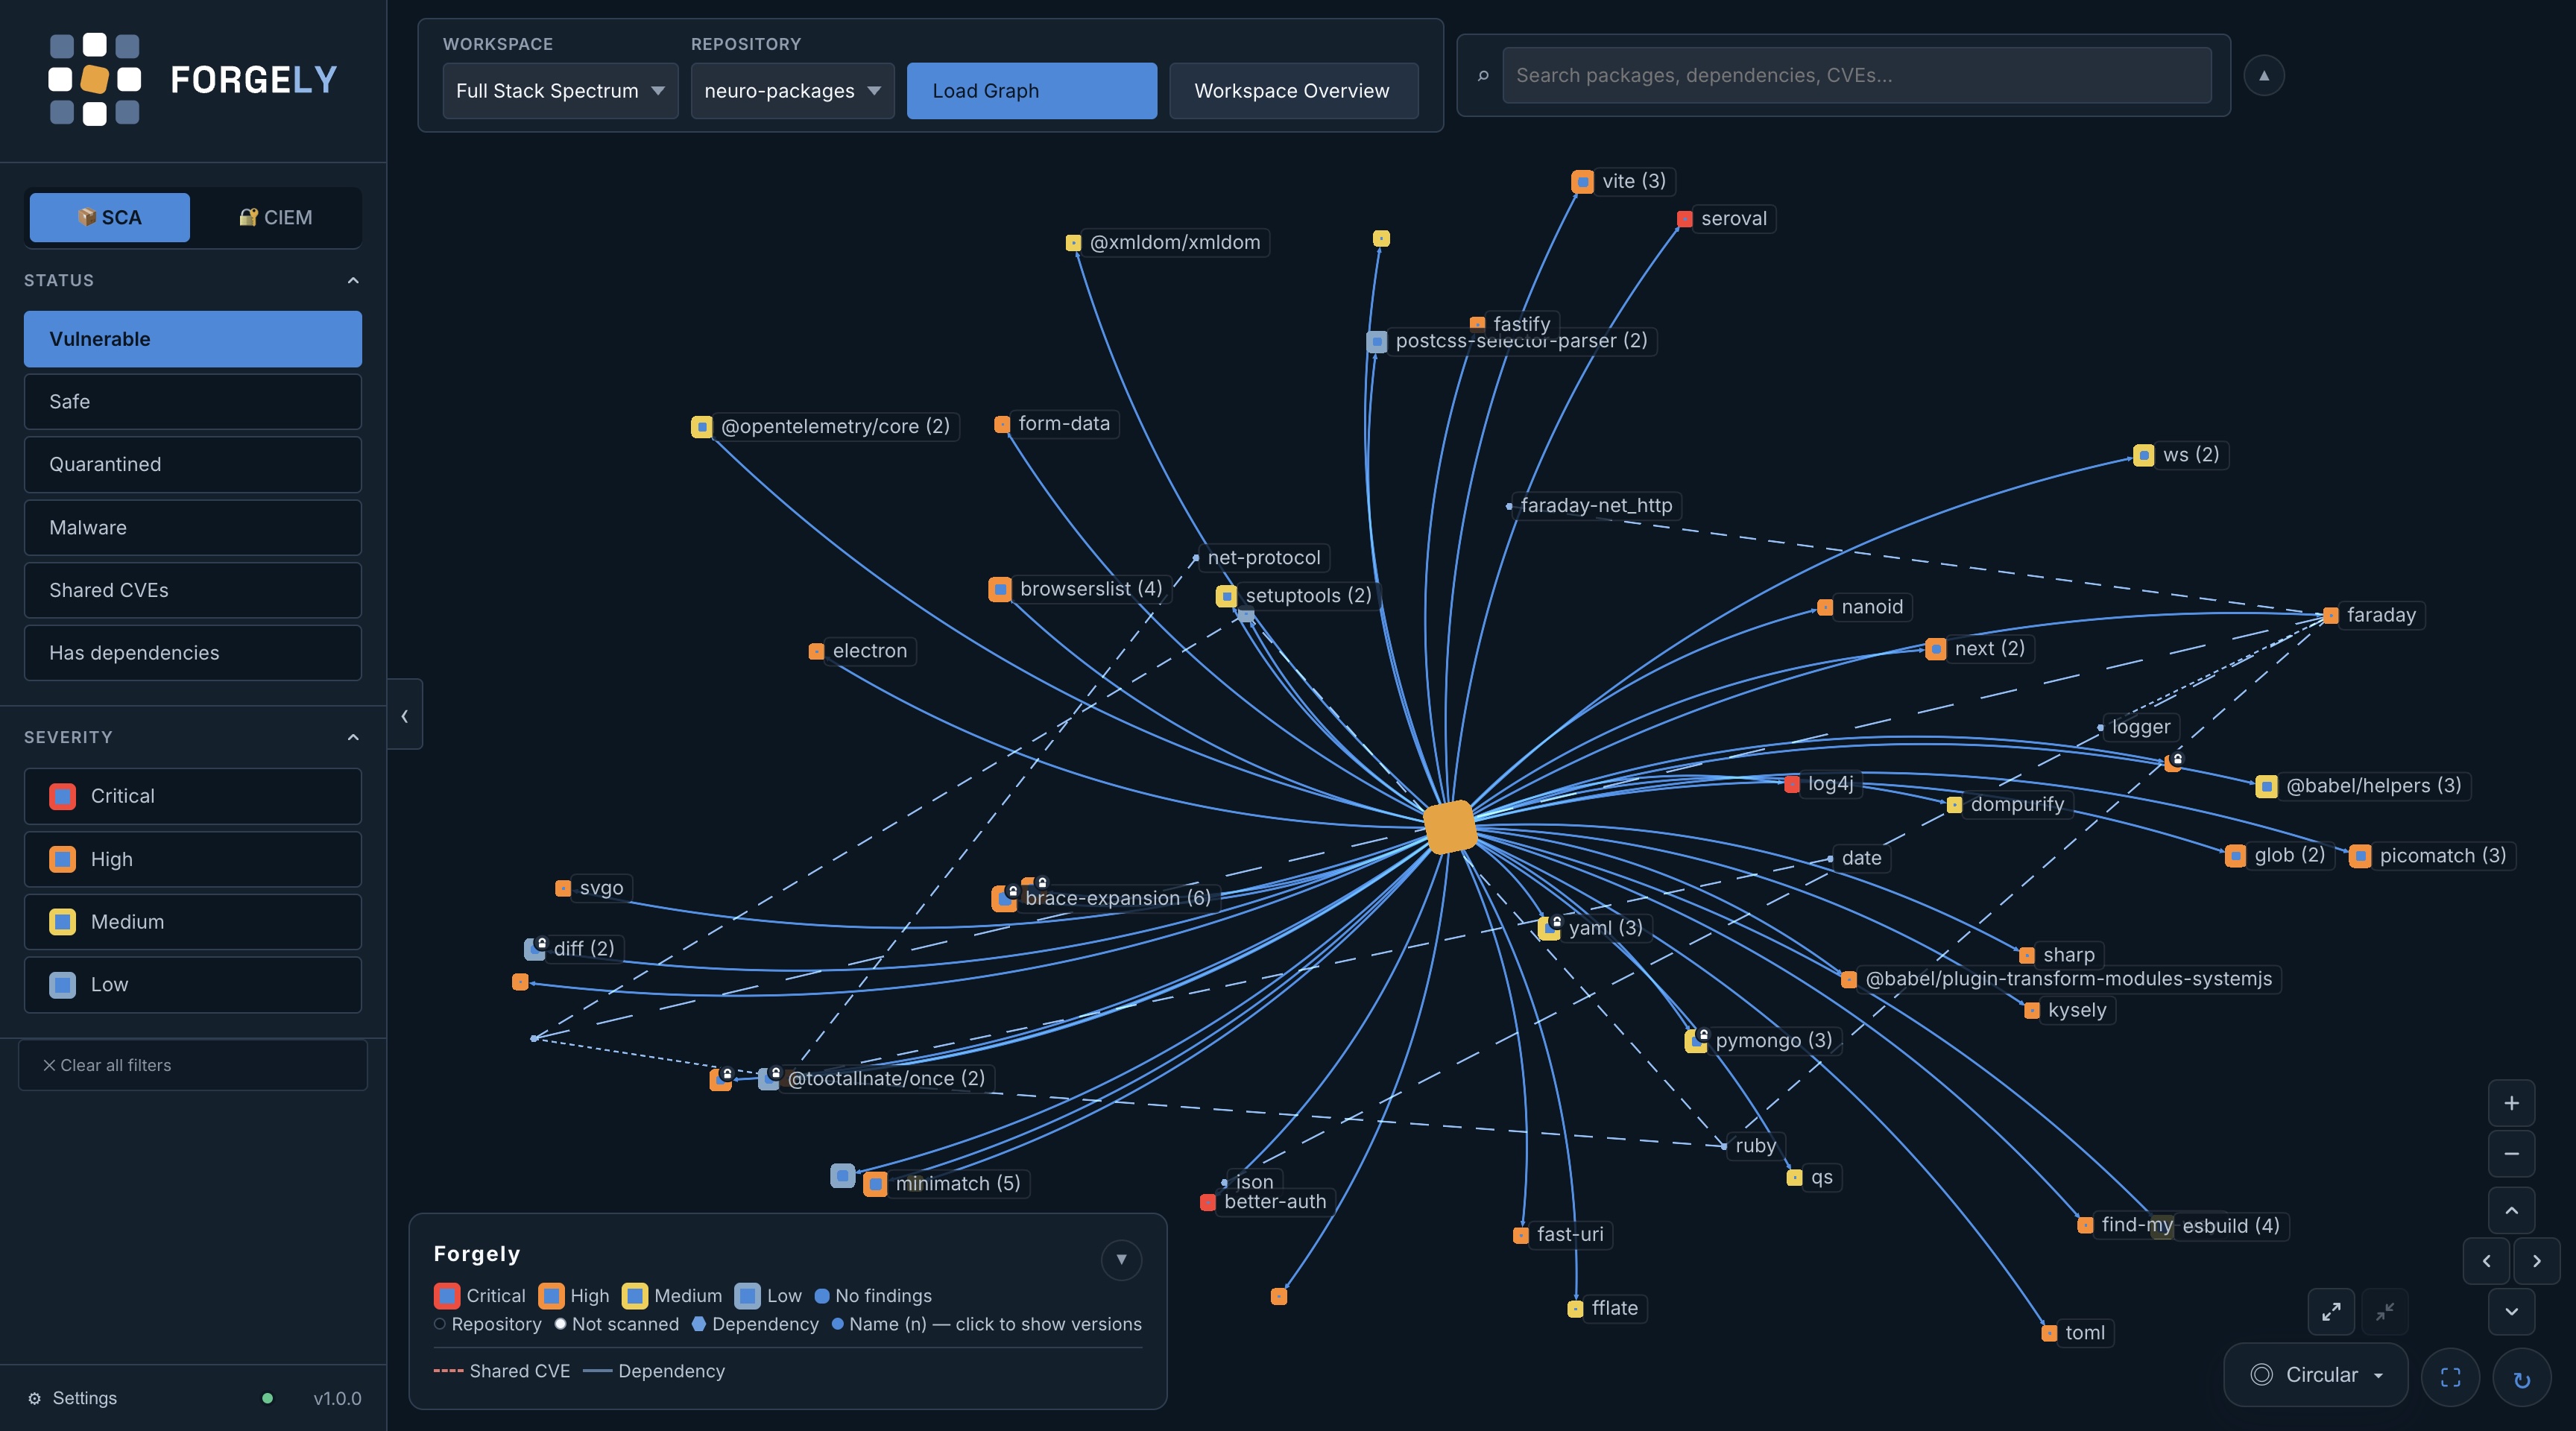
A security graph visualisation engine for Cloudsmith artifact repositories. It covers two cloud-native security disciplines — SCA and CIEM — and renders them as interactive, colour-coded graphs, so DevOps and Security teams can see blast radii, transitive risk and access exposure at a glance.
Quick start
docker run -d \
  --name forgely \
  -p 8000:8000 \
  -v forgely-cache:/data \
  fullstackspectrum/forgely:latest
Open http://localhost:8000 and add your Cloudsmith API key under Settings → Connection. The key is stored in your browser, not in the image.
-p 8000:8000is required. Without it the container starts and reports healthy, but nothing reaches it.
docker compose
services:
  forgely:
    image: fullstackspectrum/forgely:latest
    ports:
      - "8000:8000"
    volumes:
      - forgely-cache:/data
    restart: unless-stopped

volumes:
  forgely-cache:
What it shows
SCA — Software Composition Analysis
- Which packages carry known CVEs, across every repository in a workspace
- The blast radius of a vulnerability — which dependent packages are transitively exposed
- Attack paths from a client tool through the registry to a CVE
- Package metadata per format: digests, tags, identifiers, architecture, uploader
CIEM — Cloud Infrastructure Entitlement Management
- Which members, service accounts and teams can reach which repositories
- Entitlement tokens, upstream proxies and connected repositories
- Over-privileged and unexpected access paths between identities and resources
Combining the two lets you cross-reference a vulnerable package with the identities that can write to or download from the repository hosting it — the step that turns a CVE into an assessment of actual exposure.
Tags
| Tag | Meaning |
|---|---|
latest | Most recent release |
1.0.0-beta.11 | A specific version. Pin this for anything reproducible |
Platforms: linux/amd64, linux/arm64.
Windows users are covered by linux/amd64 — Docker Desktop runs Linux
containers through WSL2, so no separate Windows image is needed.
Configuration
Everything is optional. Forgely runs with no configuration at all and takes an API key through the UI.
| Variable | Description |
|---|---|
CLOUDSMITH_API_KEY | A server-side key, if you would rather every visitor to this instance share one instead of entering their own |
CLOUDSMITH_OWNER | Default workspace slug, pre-selected on load |
CLOUDSMITH_REPO | Default repository slug, pre-selected on load |
FORGELY_CACHE_PATH | Scan cache location (default /data/scans.db) |
CORS_ORIGINS | Only needed if you serve the frontend from another origin. Not required here — one container serves both |
Volume
Mount /data to keep the vulnerability scan cache between runs. It is keyed on
each package's scan completion time rather than a TTL, so entries never go
stale — and a warm cache turns a cold graph build of several thousand packages
into a local read instead of thousands of API calls.
Image
- Distroless. Built on Chainguard images.
No shell and no package manager, so
docker exec … shwill not work — usedocker logs. - Scans clean.
trivy image fullstackspectrum/forgelyreports no vulnerabilities at any severity. - Non-root. Runs as uid 65532.
- Single container. The backend serves the built frontend, so there is no second service and no CORS to configure.
An API key is never baked into the image.
Notes
Not affiliated with Cloudsmith. This is an independent, community-developed tool. It is not endorsed or supported by Cloudsmith Ltd, and is provided "as is", without warranty of any kind. Cloudsmith Ltd accepts no responsibility or liability for any loss, damage or issues arising from its use. Use at your own risk.
Built with AI assistance. A large share of this code was written by an AI assistant working from prompts, then reviewed and directed by a human. Treat it as you would any code you did not write line by line: read it before running it against anything you care about.
Source: https://github.com/fullstackspectrum/Forgely · Licence: Apache-2.0
Tag summary
Content type
Image
Digest
sha256:f19ed6804…
Size
38.1 MB
Last updated
about 1 month ago
docker pull fullstackspectrum/forgely