getreadystack/security-txt-cra-lint
Not affiliated with ReadyStack (readystack.dev). No new versions are published here.
342
getreadystack/security-txt-cra-lint repository overview
Not affiliated with ReadyStack (readystack.dev). No new versions are published here.
security.txt Lint - RFC 9116 + CRA contact point
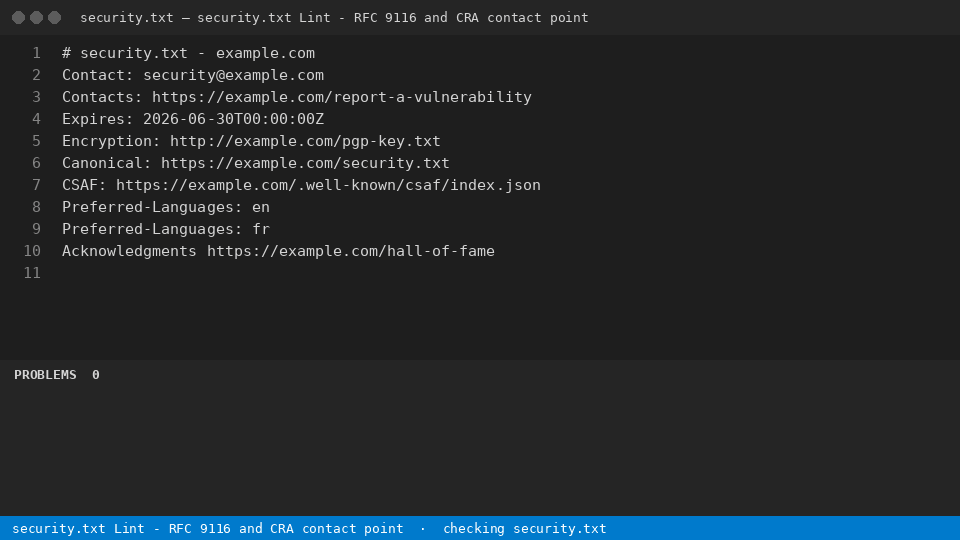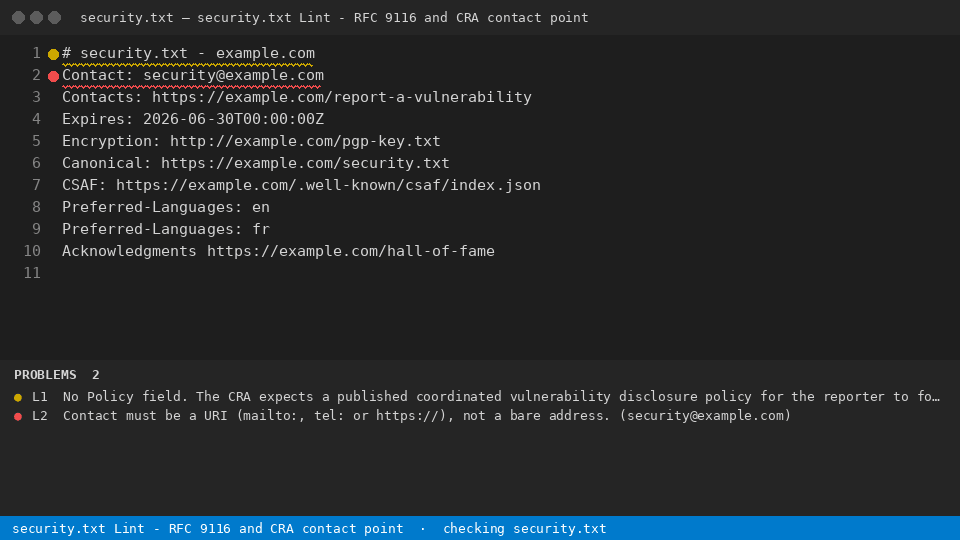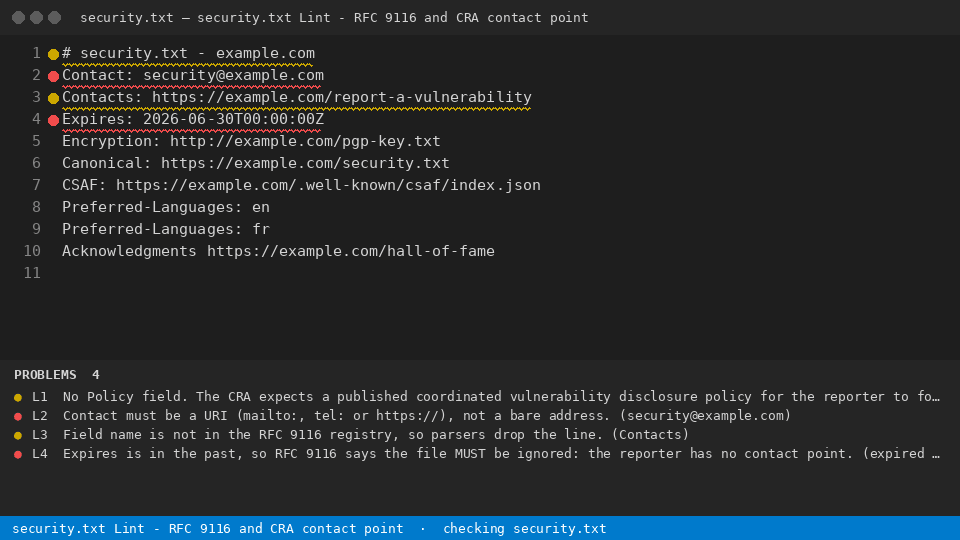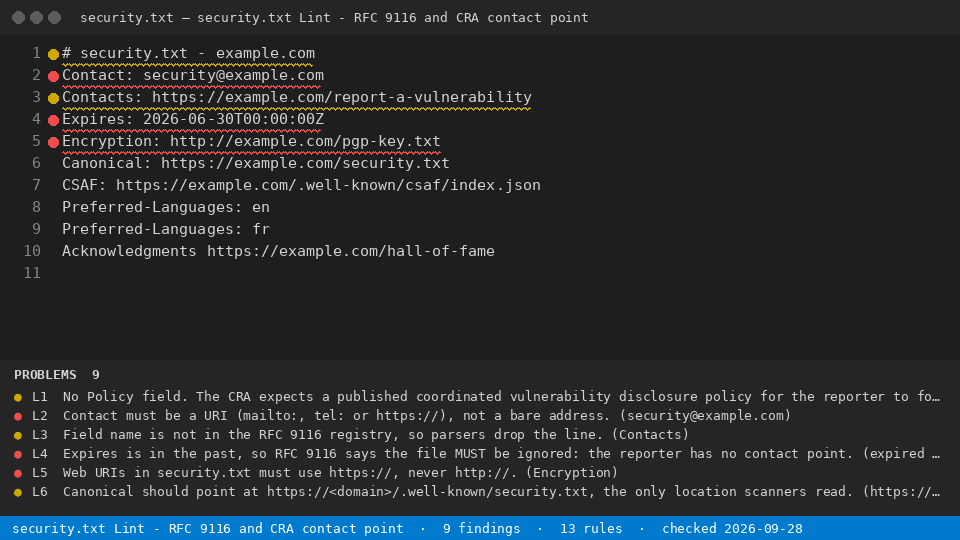
13 rules that decide whether a vulnerability report ever reaches you
Run
docker run --rm -v "$PWD":/work getreadystack/security-txt-cra-lint /work/file
The same 13 rules as the VS Code extension, in a container. Mount a folder on /work.
Free
- Lint the security.txt you have open and see every RFC 9116 and CRA contact-point finding on its exact line.
--ruleslists every rule
With a licence ($29 once)
- Scan every security.txt across the whole workspace in one pass and export a dated JSON report you keep for the audit file.
docker run --rm -e READYSTACK_LICENSE=<key> -v "$PWD":/work getreadystack/security-txt-cra-lint --dir /work --ci
A security consultant reviewing a disclosure contact and policy starts around $150 an hour
Use from an AI agent (MCP)
Claude Code · Cursor · Windsurf · any MCP client - add to your MCP config:
{ "mcpServers": { "security-txt-cra-lint": { "command": "npx", "args": ["-y", "@readystack/security-txt-cra-lint", "--mcp"] } } }
Tools: check_text and check_file (free) · check_dir (licence). The agent gets every finding with the line number.
Use in CI
- name: security.txt Lint - RFC 9116 + CRA contact point
  run: npx -y @readystack/security-txt-cra-lint --dir . --ci
(container: docker run --rm -v "$PWD:/work" getreadystack/security-txt-cra-lint --dir /work --ci)
The folder sweep, reports and CI mode need one licence — one payment, no subscription. Set READYSTACK_LICENSE=<key> or run --license <key> once.
Tag summary
Content type
Image
Digest
sha256:cebb791a2…
Size
46.1 MB
Last updated
29 days ago
docker pull getreadystack/security-txt-cra-lint