getreadystack/ssdf-attestation-workflow-audit
Not affiliated with ReadyStack (readystack.dev). No new versions are published here.
141
getreadystack/ssdf-attestation-workflow-audit repository overview
Not affiliated with ReadyStack (readystack.dev). No new versions are published here.
SSDF Attestation Audit for GitHub Actions
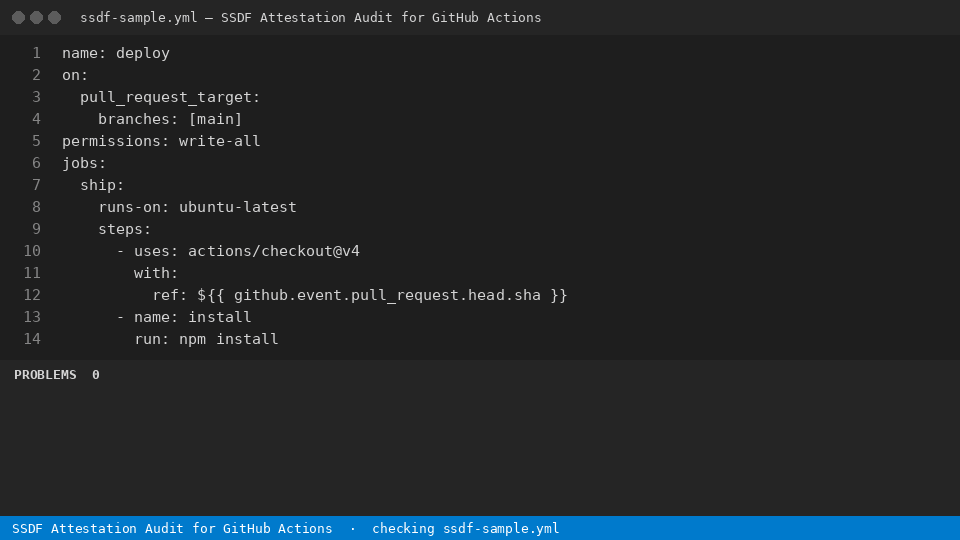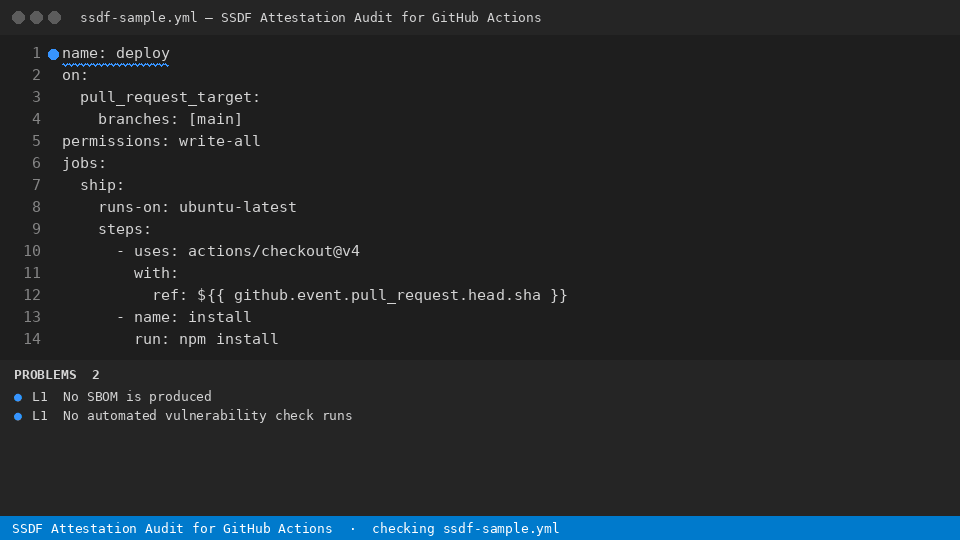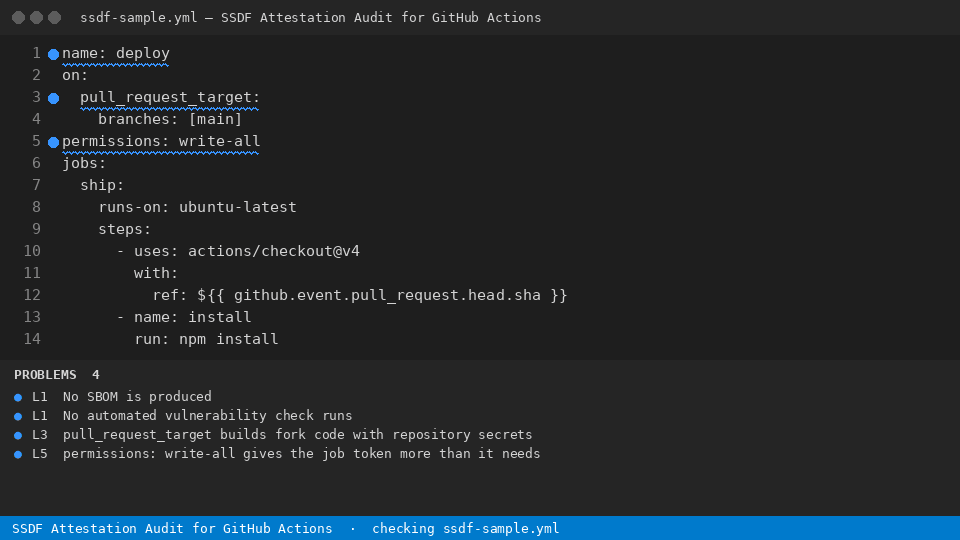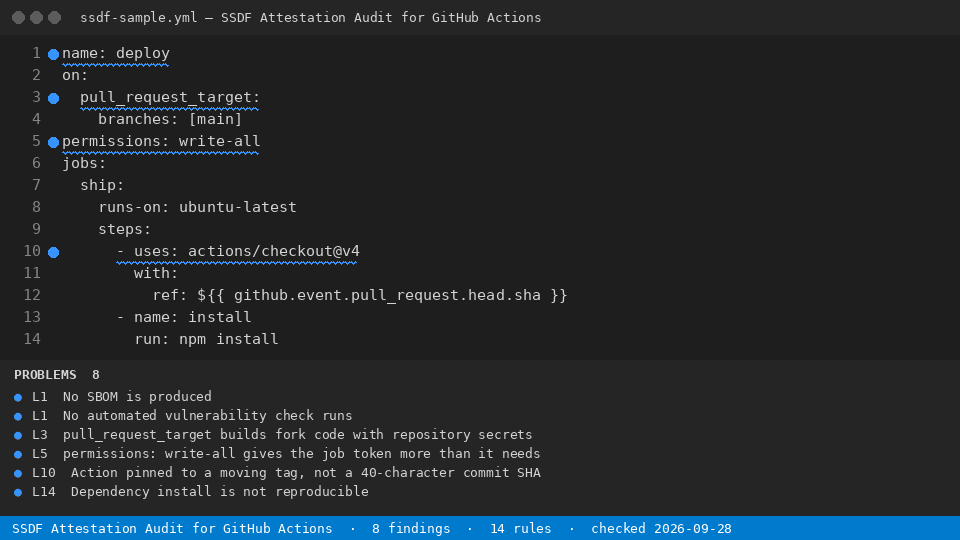
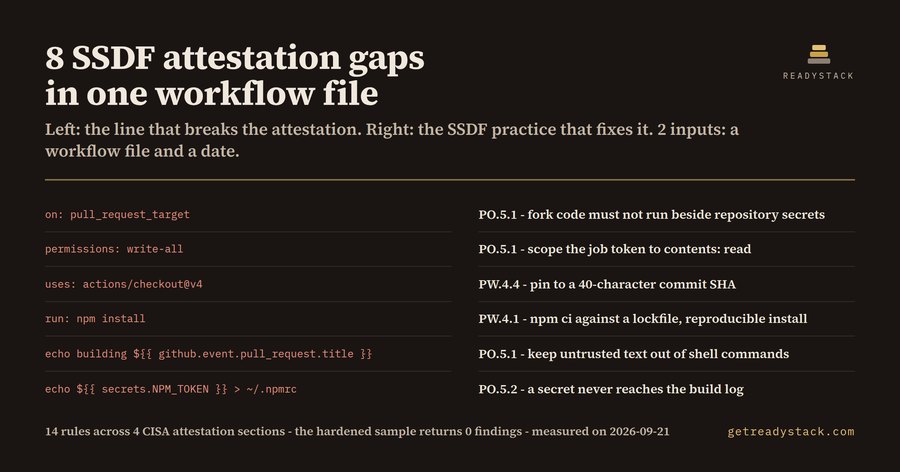
14 rules, four CISA attestation sections, one workflow file
Run
docker run --rm -v "$PWD":/work getreadystack/ssdf-attestation-workflow-audit /work/file
The same 14 rules as the VS Code extension, in a container. Mount a folder on /work.
Free
- Audit the workflow file you have open and list every attestation gap with its SSDF practice ID and the CISA form section it sits under.
--ruleslists every rule
With a licence ($29 once)
- Audit every workflow in the repository at once and export one dated evidence table mapped to all four attestation sections.
docker run --rm -e READYSTACK_LICENSE=<key> -v "$PWD":/work getreadystack/ssdf-attestation-workflow-audit --dir /work --ci
A US application-security contractor bills roughly 150-250 an hour to review and re-pin a release pipeline by hand.
Use from an AI agent (MCP)
Claude Code · Cursor · Windsurf · any MCP client - add to your MCP config:
{ "mcpServers": { "ssdf-attestation-workflow-audit": { "command": "npx", "args": ["-y", "@readystack/ssdf-attestation-workflow-audit", "--mcp"] } } }
Tools: check_text and check_file (free) · check_dir (licence). The agent gets every finding with the line number.
Use in CI
- name: SSDF Attestation Audit for GitHub Actions
  run: npx -y @readystack/ssdf-attestation-workflow-audit --dir . --ci
(container: docker run --rm -v "$PWD:/work" getreadystack/ssdf-attestation-workflow-audit --dir /work --ci)
The folder sweep, reports and CI mode need one licence — one payment, no subscription. Set READYSTACK_LICENSE=<key> or run --license <key> once.
Tag summary
Content type
Image
Digest
sha256:7d59da98f…
Size
46.1 MB
Last updated
23 days ago
docker pull getreadystack/ssdf-attestation-workflow-audit