offensivedockerfiles/striker
Striker is an offensive information and vulnerability scanner.
Image
0
964
offensivedockerfiles/striker repository overview

Striker
Striker is an offensive information and vulnerability scanner.
Features
Just supply a domain name to Striker and it will automatically do the following for you:
- Check and Bypass Cloudflare
- Retrieve Server and Powered by Headers
- Fingerprint the operating system of Web Server
- Detect CMS (197+ CMSs are supported)
- Launch WPScan if target is using Wordpress
- Retrieve robots.txt
- Check if the target is a honeypot
- Port Scan with banner grabbing
- Dumps all kind of DNS records
- Generate a map for visualizing the attack surface
- Gather Emails related to the target
- Find websites hosted on the same web server
- Find hosts using google
- Crawl the website for URLs having parameters
- SQLi scan using online implemention of SQLMap (takes < 3 min.)
- Basic XSS scanning
Install
git clone https://github.com/UltimateHackers/Striker
cd Striker
pip install -r requirements.txt
python striker.py
Docker
git clone https://github.com/UltimateHackers/Striker
cd Striker
docker build -t striker .
docker run -it striker:latest
Screenshots


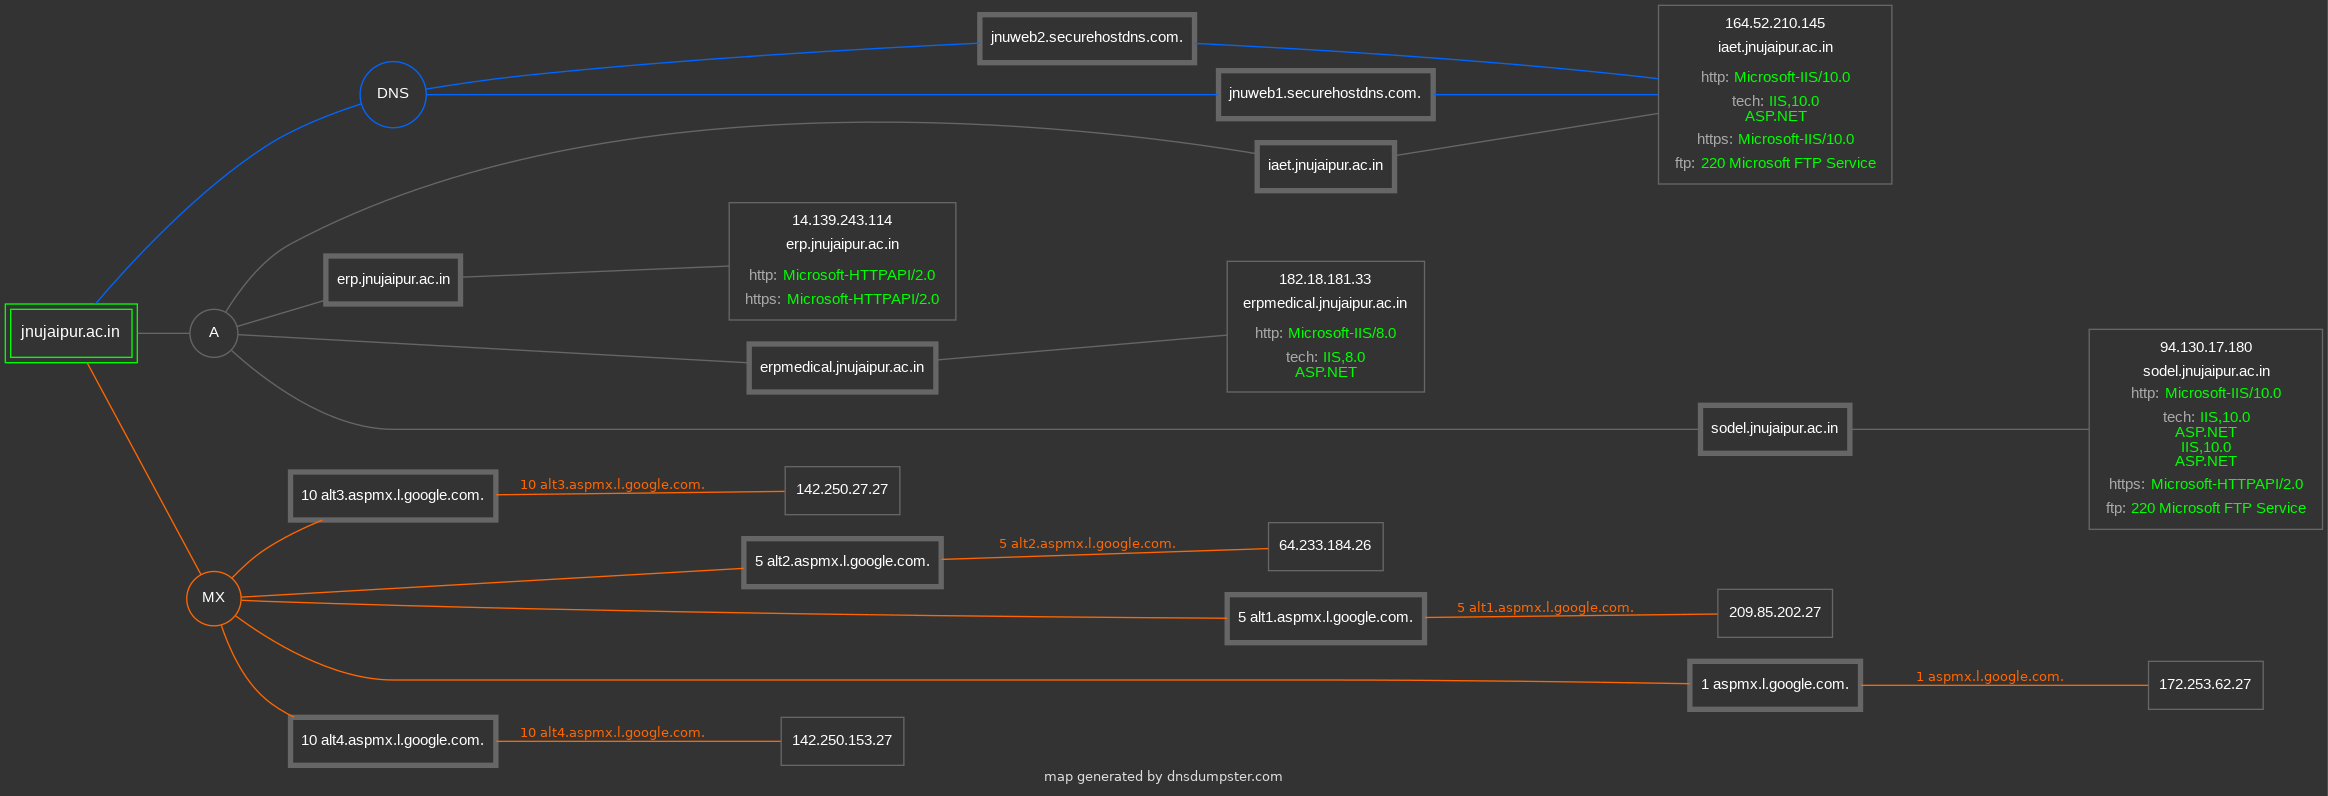 Want to see what else it can do? Try it yourself.
Contribute
If you want to contribute to this project, report any bugs you encounter and help me add more features to it.
Tag summary
Content type
Image
Digest
Size
84.3 MB
Last updated
about 8 years ago
docker pull offensivedockerfiles/striker