tolerantsoftware/mpm
Official Images for TOLERANT MPM
481
tolerantsoftware/mpm repository overview
Quick reference
- Maintained by: https://www.tolerant-software.de/
- Where to get help: [email protected]
- Release Notes: https://www.tolerant-software.de/en/products/tolerant-mpm/product-support/
Product Overview
Permission marketing is all about consent
You want to send a newsletter? Contact customers by phone? For this, you first need the permission of your customers. You need this permission to contact them not only for direct contact, but also if you want to collect and analyze data. Do you want to use data analysis to find out which product recommendation is promising or when the best time to buy is? You may not collect the data for this without the consent of your customer.
With TL MPM you can collect, save, archive, manage and prove these consents.
Collecting consent from the customer
The so-called permission marketing includes different variants of consent. The simplest and best known is the double opt-in process, by which prospective customers confirm that they wish to receive a newsletter. Each newsletter must also contain a notice or link for possible unsubscription. Further customer contacts are not permitted on this basis.
Federal Data Protection Act and EU General Data Protection Regulation.
In May 2018, a new EU Basic Data Protection Regulation came into force. For this and for more complex activities than a newsletter, additional declarations of consent must be obtained from the customer. With TL MPM, you manage and store all necessary consents, declaration texts and consent options clearly and quickly accessible – if required in all necessary languages.
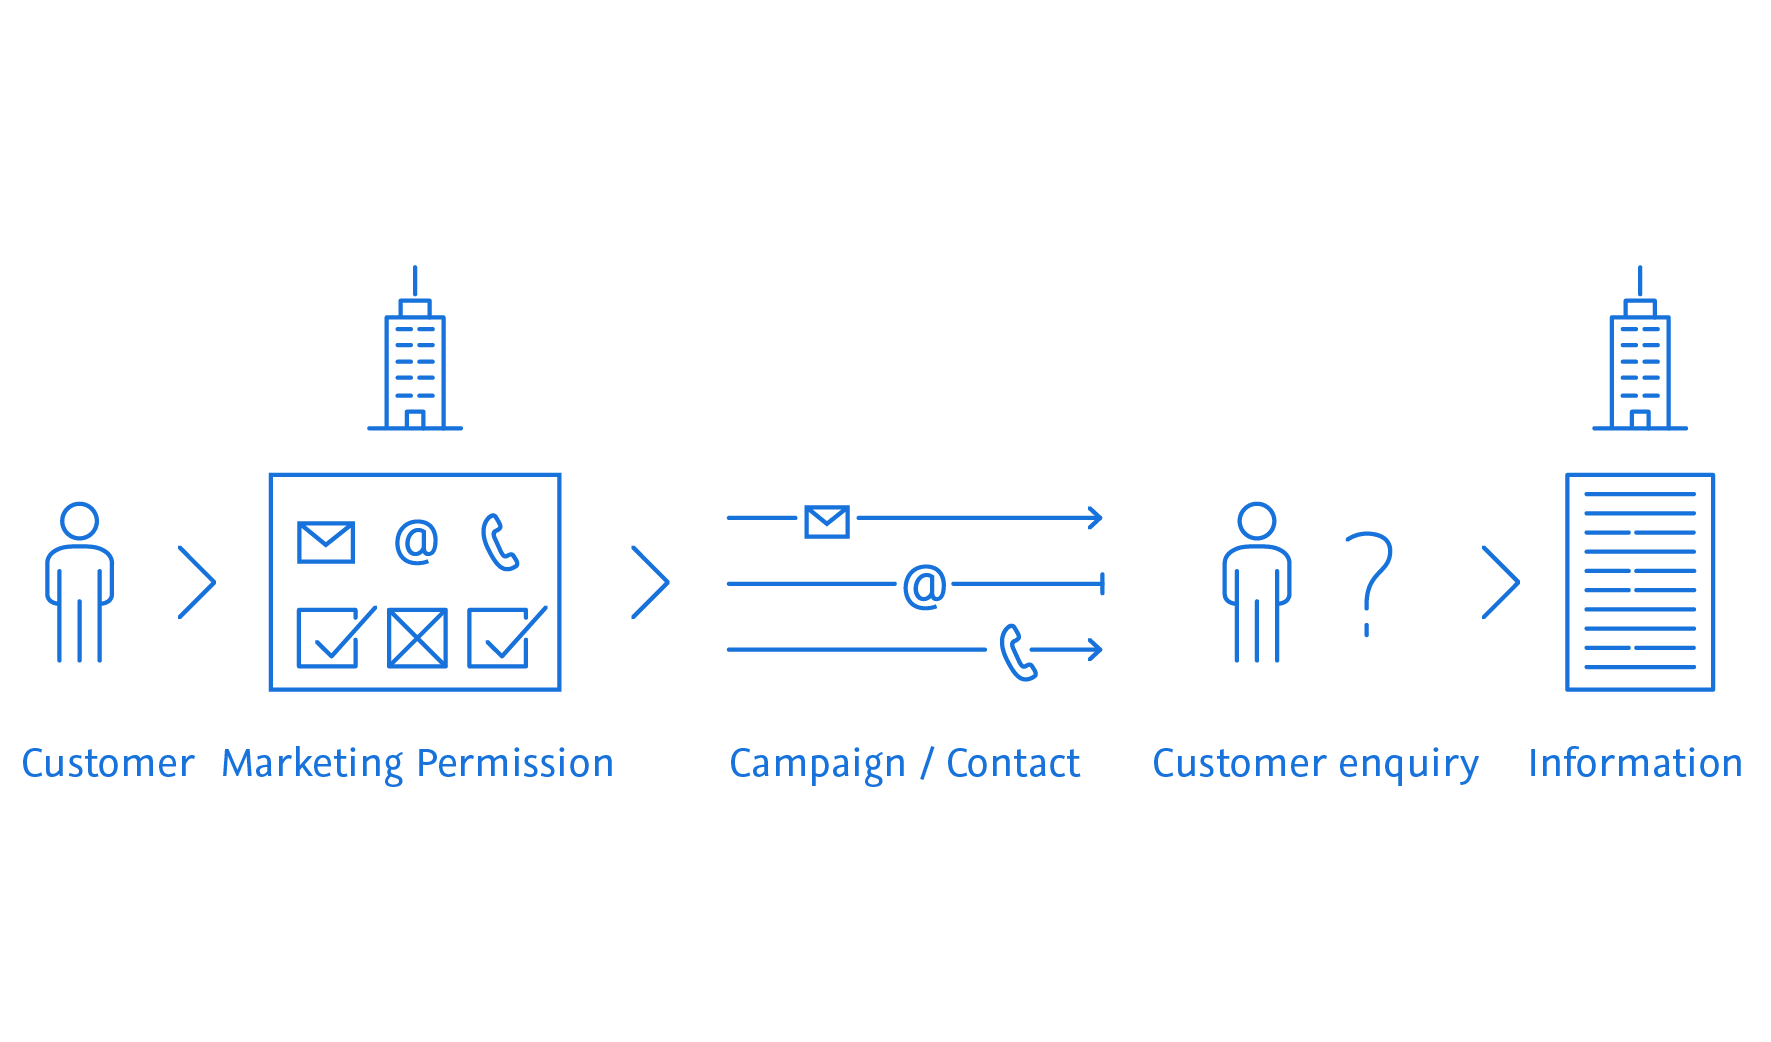
The customer’s consent passes through several stages in the process:
-
Obtain the consent of your customers – without gaps With TL MPM you know exactly who has already agreed to the marketing contact and who has not. And therefore only re-contact those customers who have not yet decided.
-
Reliably implement customer decisions TL MPM informs you whether the customer has given the required consent for a contact, for data sharing or for data use. If the customer changes his mind, you can take this into account immediately and comprehensively – e.g. if customers demand a complete stop of all further advertising.
-
On request, you can provide complete proof of consent Your customer demands information about the use of his data? According to the Federal Data Protection Act and the EU General Data Protection Regulation, you are obliged to provide this proof. With TL MPM the documentation is easy and complete. You can quickly and clearly provide information about the sources of the data, the collected consents and the use and further processing of the data.
TL MPM is an important tool for modern and successful omni-channel marketing: With TL MPM’s consent management, the seamless collection and application of marketing permissions works easily, quickly and clearly.
Compliance software: optimizing management systems and securely mapping organizational structures
In many areas, the use of special and intuitive software makes it possible to significantly reduce costs and save time. It is important that the software solutions used can be operated by all employees without exception and without any problems. Good compliance software enables secure documentation and mapping of processes in management systems, for example. It is important that the software works in such a way that it meets the requirements of applicable standards. A selection of important functions is therefore required for the effective design of the compliance management system.
Important compliance software functions: Seamless documentation of management processes
When looking for compliance software for management systems, you should always take a look at the functions and the associated details. It is important that your company and the processes that take place here can be mapped without major gaps and can therefore be concretized. Thanks to the comprehensive functions, the software itself is able to carry out a risk assessment and present this in a comprehensible manner. Measures can then be derived from this, which can be used to monitor effectiveness.
Legally compliant documentation is important
The requirements to which companies are exposed in a wide variety of areas are increasing inexorably. For many companies, the associated effort is increasingly becoming a challenge. This in turn ensures that compliance software for management systems is more in demand than ever. One of the most important criteria in the selection process is the design and processing of documentation. This should be complete and legally compliant. Furthermore, when selecting the software, care should be taken to ensure that it is constantly updated. This is the only way to adapt functions and handling to your own needs and the company’s requirements without major problems.
TOLERANT MPM image
Usage
Notes
- The container needs licenses to run properly. For proper test licences please contact [email protected].
- The required configuration files can be found on the official MPM GitHub
Starting and stopping can be managed using a simple docker compose file. Here is an example:
services:

  backend:
    image: ${TMPM_DOCKER_REGISTRY}/mpm:${TMPM_VERSION}
    mem_limit: 2g
    environment:
      - TZ=${TZ}
      - JVM_OPT_ACTIVE_PROCESSOR_COUNT=4
      # enable the metrics export for prometheus
      - TMPM_PROMETHEUS_METRICS_ENABLED=true
      # identity provider settings
      - TOLERANT_REALM=${TOLERANT_REALM}
      - TOLERANT_CLIENT_ID=${TOLERANT_CLIENT_ID}
      - IDENTITY_PROVIDER_URL=${IDENTITY_PROVIDER_URL}
      # security
      - SECURITY_ENABLED=${SECURITY_ENABLED}
    restart: unless-stopped
    volumes:
      # Example for custom configuration via volume:
      # - mpm-config:/opt/tolerant/config
      # persist mpm data
      - mpm-data:/opt/tolerant/data
      # persist mpm logs
      - mpm-logs:/opt/tolerant/logs
      - type: bind
        source: ./config/backend/mpm-gui_config_keycloak.json
        target: /opt/tolerant/config-default/service/mpm-gui_config.json
        read_only: true
    expose:
      - 8080
    depends_on:
      - keycloak
    extra_hosts:
      - host.docker.internal:host-gateway

  gui:
    image: ${TMPM_DOCKER_REGISTRY}/mpm-gui:${TMPM_VERSION}
    mem_limit: 512m
    environment:
      - JVM_OPT_ACTIVE_PROCESSOR_COUNT=2
      # identity provider settings
      - TOLERANT_REALM=${TOLERANT_REALM}
      - IDENTITY_PROVIDER_URL=${IDENTITY_PROVIDER_URL}
      # security
      - SECURITY_ENABLED=${SECURITY_ENABLED}
    restart: unless-stopped
    #volumes:
    # Example for custom configuration via volume:
    # - mpm-config:/opt/tolerant/config
    expose:
      - 8080
    depends_on:
      - backend
      - keycloak
    extra_hosts:
      - host.docker.internal:host-gateway

  openssl:
    image: tolerantsoftware/openssl
    build: ./config/openssl
    environment:
      - ORGANISATION_UNIT=TOLERANT MPM
    volumes:
      - ./config/nginx/ssl/certs:/etc/ssl/certs
      - ./config/nginx/ssl/private:/etc/ssl/private

  proxy:
    image: nginx:${NGINX_VERSION}-alpine
    environment:
      - NGINX_FORWARDED_FOR=${NGINX_FORWARDED_FOR}
      - IDENTITY_PROVIDER_URL=${IDENTITY_PROVIDER_URL}
      - IDENTITY_PROVIDER_PORT=${KC_PORT}
      - CERT_PRIVATE_KEY_FILENAME=ssl.key
      - CERT_FILENAME=ssl.crt
      - NGINX_SERVER_NAME=${NGINX_SERVER_NAME}
    restart: unless-stopped
    volumes_from:
      - openssl
    volumes:
      - type: bind
        source: ./config/nginx/ssl.conf.template
        target: /etc/nginx/templates/ssl.conf.template
        read_only: true
      # persist nginx logs
      - nginx-logs:/etc/nginx/logs
      # Example for ssl data in external volume
      # nginx-ssl:/etc/nginx/ssl
    ports:
      - ${NGINX_HTTPS_PORT}:8443
    depends_on:
      backend:
        condition: service_started
      gui:
        condition: service_started
      grafana:
        condition: service_started
      openssl:
        condition: service_completed_successfully
        restart: true
    extra_hosts:
      - host.docker.internal:host-gateway

  prometheus:
    image: prom/prometheus:${PROMETHEUS_VERSION}
    restart: unless-stopped
    volumes:
      - type: bind
        source: ./config/prometheus/prometheus.yml
        target: /etc/prometheus/prometheus.yml
        read_only: true
      - prometheus-data:/prometheus
    expose:
      - 9090
    depends_on:
      - backend

  grafana:
    image: grafana/grafana:${GRAFANA_VERSION}
    restart: unless-stopped
    volumes:
      - ./config/grafana/datasources:/etc/grafana/provisioning/datasources
      - ./config/grafana/dashboards:/etc/grafana/provisioning/dashboards
      - grafana-data:/var/lib/grafana
    environment:
      - GF_SECURITY_ADMIN_USER=tolerant
      - GF_SECURITY_ADMIN_PASSWORD=tolerant
    ports:
      - ${GRAFANA_PORT}:3000
    depends_on:
      - prometheus
  # in case you have your own identity provider, remove postgres and keycloak
  postgres:
    image: postgres:${POSTGRES_VERSION}
    restart: unless-stopped
    volumes:
      - postgres-data:/var/lib/postgresql/data
    environment:
      POSTGRES_DB: keycloak
      POSTGRES_USER: keycloak
      POSTGRES_PASSWORD: password

  keycloak:
    image: keycloak/keycloak:${KC_VERSION}
    command: start-dev --import-realm
    restart: unless-stopped
    volumes:
      - type: bind
        source: ./config/keycloak/import
        target: /opt/keycloak/data/import
        read_only: true
    environment:
      - KC_DB=postgres
      - KC_DB_SCHEMA=public
      - KC_DB_USERNAME=keycloak
      - KC_DB_PASSWORD=password
      - KC_DB_URL_HOST=postgres
      - KC_DB_URL_PORT=5432
      - KC_BOOTSTRAP_ADMIN_USERNAME=admin
      - KC_BOOTSTRAP_ADMIN_PASSWORD=admin
      - KC_HOSTNAME_STRICT=false
      - KC_HTTP_ENABLED=true
      - TOLERANT_CLIENT_ID=${TOLERANT_CLIENT_ID}
      - TOLERANT_REALM=${TOLERANT_REALM}
      - TMPM_DEFAULT_TENANT=${TMPM_DEFAULT_TENANT}
    ports:
      - ${KC_PORT}:8080
    depends_on:
      - postgres

volumes:
  nginx-logs:
  mpm-logs:
  mpm-data:
  grafana-data:
  prometheus-data:
  postgres-data:
  # Examples for external created volumes with custom configuration
  # mpm-config:
  #   external: true
  # Example volume for ssl data of the nginx container
  # nginx-ssl:
  #   external: true
Starting the services
The services can be started using the following command:
docker compose up -d
Stopping the services
Running services can be stopped using the following command:
docker compose down
License
TOLERANT MPM is licensed under a commercial license. This means that the software can only be used for commercial purposes, and that the user must have a valid license to use the software. To get a valid license, please contact [email protected]
Tag summary
Content type
Image
Digest
sha256:18f024d87…
Size
108 MB
Last updated
3 months ago
docker pull tolerantsoftware/mpm